Tag: privacy

Why Did a Puerto Rico Healthcare Company Pay $2.7 Million in HIPAA Penalties When It Doesn’t Even Treat Patients?

The most common HIPAA violation in medical offices isn’t caused by hackers. It is one caused by never writing one specific document.
In December 2024, the U.S. Department of Health and Human Services’ Office for Civil Rights (“OCR”) announced a $250,000 settlement with Inmediata Health Group, a “clearinghouse” (an intermediary that converts medical claims into the standard format insurance plans require) based in Puerto Rico that processes data for physicians, dentists, hospitals, laboratories, and health plans across the island.

What happened? Between May 2016 and January 2019, the health information of 1,565,338 people held by Inmediata became publicly accessible on the internet due to a website misconfiguration. That information included names, dates of birth, addresses, Social Security numbers, medical diagnoses, and treatment information — all indexed and accessible through Google.

OCR identified the root cause: Inmediata had never conducted an adequate risk analysis, and it wasn’t monitoring activity on its information systems.

The total cost of this website error was far more than $250,000. Between the OCR settlement, a $1.4 million multi-state settlement with 32 state attorneys general and Puerto Rico, and a $1,125,000 class-action payout, the incident cost Inmediata at least $2.7 million.

$2.7 million in penalties for not having a document required since 2005.

What Is a Risk Analysis, and Why Is It Mandatory?

HIPAA’s Security Rule, at 45 C.F.R. § 164.308(a)(1)(ii)(A), requires every covered entity and business associate to conduct “an accurate and thorough assessment of the potential risks and vulnerabilities” to the confidentiality, integrity, and availability of the electronic health information it handles.

There’s a technical detail here that many people overlook. The Security Rule splits its requirements into 2 categories: requiredand addressable. Required specifications must be implemented by every covered entity and business associate. There’s no flexibility, no alternative, and no exception for the size of the practice. A solo physician’s office has the same obligation as a hospital.

Addressable specifications, on the other hand, do allow flexibility: if your office determines a measure isn’t reasonable given its size, you can document why and adopt an alternative instead.

The Security Rule was designed to account for the size and complexity of your operation, your technical infrastructure, the cost of security measures, and the probability and severity of your risks. A small practice doesn’t need the same analysis as a hospital system. But it needs one.

OCR Is Actively Looking for These Assessments

In October 2024, OCR launched an enforcement initiative dedicated exclusively to this requirement, called the Risk Analysis Initiative. By 2026, it had already announced roughly a dozen enforcement actions.

The reasoning behind focusing on this is fairly simple. These are straightforward cases for OCR: the question they need to answer is: do you have this document or not?

If you’re a HIPAA-covered entity, you need to understand that, if OCR opens an investigation, the first document they’ll ask for is your risk analysis — and most offices can’t produce one.

Being a small practice or business doesn’t protect you from being sanctioned. For example, Bryan County Ambulance Authority (“BCAA”), an entity serving just over 14,000 people, was the first case under this initiative. It settled with HHS for $90,000 following a ransomware attack. The investigation concluded that BCAA had never conducted an adequate risk analysis. Similarly, West Georgia Ambulance, an ambulance company in Carroll County, Georgia, paid $65,000 to HHS in a settlement for failing to conduct a risk analysis, failing to maintain a security awareness training program for its employees, and failing to implement policies and procedures for the Security Rule. 500 individuals were affected by this incident.

OCR recently expanded its investigative focus from “risk analysis” to “risk management.” As a result, the question is no longer just “do you have the document?” but “can you show you acted on what you found?” An analysis done 5 years ago, filed away and never acted on, could today be seen as nearly as bad as having no analysis at all.

Why Should This Matter to You?

Here are at least 4 reasons:

First: ignorance isn’t a defense. The Security Rule has been in force for more than 20 years. OCR has been explicit in concluding that not knowing the Rule doesn’t excuse anyone. At best, it might lower the penalty, but it will not eliminate it.

Second: you face double legal exposure. Since the federal HITECH Act was passed, state attorneys general have independent authority to bring civil actions for HIPAA violations. The Inmediata case demonstrates this clearly: OCR collected $250,000 and the multi-state coalition collected $1.4 million for the same underlying facts. These are separate proceedings.

Third: Puerto Rico has an additional obligation. 2005’s Law 111, as amended, covered previously in this blog, applies to you even if you are subject to HIPAA. Its Article 2 defines “personal information file” to expressly include “medical protection protected by the HIPAA Act.” Consequently, complying with the federal notification does not relieve you of the local obligation. Law 111 requires you to report the security breach to DACO (Puerto Rico’s Department of Consumer Affairs) within a non-extendable 10-day period from detecting the breach. DACO is then required to make a public announcement of the incident within the following 24 hours. Compare this with HIPAA, which gives you up to 60 days to notify affected individuals. Puerto Rico’s clock runs much faster and does not give any extensions. Its fines range from $500 to $5,000 per violation, and they do not prevent those affected from separately suing you for damages. We previously explained this law here. Separately, Section 5 of the Federal Trade Commission (“FTC”) Act covers privacy and security representations made to the public, including what your own website says. Between OCR, the state’s attorneys general, DACO and the FTC, a single incident can lead to 4 simultenaous open legal proceedings against you. 

Fourth: This one is important, but one that doesn’t show up in any of these settlements. The first thing your cyber-liability insurer will likely ask for if you ever need to file a claim over a data breach is your risk analysis. If you don’t have one, a denied claim could cost you far more than the fine itself.

How Can You Comply with the Law?

A risk analysis isn’t a form you fill out in an afternoon, but it also doesn’t require hiring an international consulting firm. OCR’s guidance identifies the elements it should contain:

  1. Scope — every system that creates, receives, maintains, or transmits electronic health information. That includes the personal cell phone your front-desk staff uses to schedule appointments, the computer at home, and your website.
  2. Data collection — where that information lives, who touches it, where it travels.
  3. Threats and vulnerabilities — from ransomware to a laptop left in a car.
  4. Current controls — what you have in place today to mitigate each risk.
  5. Likelihood that each threat will materialize.
  6. Impact if it does.
  7. Risk level resulting from combining the two above.
  8. Documentation — in writing, with dates.
  9. Periodic review — this isn’t a one-time event.

Here are 3 practical recommendations that you can implement:

  1. Use the free federal government tool. HHS publishes the Security Risk Assessment Tool, designed specifically for small and mid-sized practices. It walks you through the elements in plain-language questions, and it’s free.
  2. Don’t forget to review your website. In risk analyses, many medical offices overlook their own website — the security of contact forms, tracking pixels, plugins, and hosting. HHS’s tool won’t ask you about this; you have to add it yourself.
  3. Document the corrective actions you’ve taken, not just the findings. With OCR’s shift toward risk management, a dated record of what you found, what you did about it, and when, is just as important as the analysis itself.
  4. Encrypt your devices, even though HIPAA doesn’t require it. Encryption is an “addressable” implementation specification under the HIPAA Security Rule. However, under Puerto Rico’s Law 111, the duty to notify is triggered only if the information was not protected by cryptographic keys beyond a password. Translation: losing a laptop with strong encryption, whose keys were not compromised, doesn’t start the 10-day clock or trigger DACO’s public announcement. This is one of the few measures that can buy you protection under 2 laws at once.

The Bottom Line

The Inmediata case isn’t a story about a sophisticated hack. It was a multimillion-dollar penalty for a website misconfiguration that nobody caught because nobody was checking. That’s exactly what a risk analysis exists to prevent.

If your office handles electronic health information — and if you use electronic billing, email, or a records system, you do — you’ve had this obligation since day one. It doesn’t matter whether you have 2 employees or 200.

The question worth asking today isn’t whether you’ll eventually be investigated. It’s simpler than that: if OCR asked for your risk analysis tomorrow morning, could you produce it?

If your answer is “no” — or “we did one years ago and I don’t know where it is” — it’s worth addressing now, before it becomes a matter of enforcement instead of planning, and before it costs you hundreds of thousands of dollars in penalties, and before your name ends up in newspapers and blogs across Puerto Rico and the mainland U.S. for failing to protect your patients’ information.

Do you have questions about whether your medical practice complies with this HIPAA rule? You can schedule a consultation with us today. We’re here to help.

About the Author

Jaime Farrant is an attorney admitted to practice law in Puerto Rico, New York, Maryland, and the District of Columbia, with an LL.M. in International Law, focusing on privacy, cybersecurity, and AI regulation for businesses and healthcare providers.

ADVERTISING MATERIAL. This article constitutes advertising as defined under the rules of professional conduct in effect in New York (22 NYCRR 1200.7.1 and 1200.7.3), Maryland (Rule 19-307.1 and 19-307.2), and the District of Columbia (D.C. Rules of Professional Conduct 7.1), as well as the Puerto Rico Rules of Professional Conduct (Rules 7.1–7.3). It does not constitute solicitation of known prospective clients who need legal services in a particular matter. Rather, it is general information directed to the public about the practice of law and available legal services. No attorney-client relationship is created by reading this article or by contacting the author.
Can I be sued over an algorithm that I didn’t even program?

Learn how the settlement Meta reached with 52 attorneys general could set a standard that impacts your business.

The United States has no federal artificial intelligence statute. There is no American equivalent of the EU AI Act, no agency that certifies AI models, and no registry of high-risk systems. And yet, on August 26, 2026, Meta — the parent company of Facebook, Instagram and WhatsApp, among others — agreed to subject Instagram and Facebook to an algorithmic governance regime with mandatory error thresholds, annual third-party testing, and an independent auditor who reports to state attorneys general.

It did not take a federal AI law to get there. Instead, it required the political will of a bipartisan coalition of state attorneys general determined to litigate against Meta, and that litigation produced a settlement agreement whose effects will be felt across every state and territory, Puerto Rico included.

That is the point worth absorbing for anyone working in AI governance: while we waited for comprehensive federal legislation, algorithmic regulation in the United States arrived through consumer protection litigation.

What was the case that led to this outcome?

The settlement was reached inside a consolidated proceeding, In re Social Media Adolescent Addiction/Personal Injury Products Liability Litigation (MDL 3047, Northern District of California), which consolidated several state lawsuits against Meta on 2 legal theories:

  1. Unfair and deceptive practices, under what are known as state “UDAP” statutes (Unfair and Deceptive Acts or Practices). The states alleged that Meta designed its platforms to maximize the time adolescents would spend on them — through notification mechanics, infinite scrolling, and social rewards — while publicly representing that its products were safe and that its protective tools worked as advertised.
  2. COPPA violations. COPPA is the federal privacy statute protecting children under 13, and the states alleged Meta collected children’s data without verifiable parental consent, among other failures.

Meta denied all liability, and the agreement signed last week contains no admission of wrongdoing. Nevertheless, Meta will pay a guaranteed minimum of roughly $12.7 billion to what may be 48 states, the District of Columbia and 3 territories — Puerto Rico among them — distributed over the next 10 years. That figure could rise, according to Meta, to approximately $18 billion if other platforms meet certain conditions.

Five pieces of AI governance hidden inside a consumer protection settlement

Beyond a payment of a magnitude that would be catastrophic for the vast majority of companies worldwide, the more significant fact may be this: under the agreement, Meta committed — potentially for the next decade — to what is arguably the first AI governance framework established inside a legal proceeding. This agreement will need to be studied by every business, and particularly by those that market to minors or that know their websites and apps are used by minors.

The governance framework the agreement establishes:

1. A model with a written error threshold.

Meta is required to deploy age estimation methods — trained classifiers, not sign-up forms — and to meet maximum false positive rates: roughly 10% for minors aged 16 and 17, and 3% for the 13-to-15 group, with wider tolerances during the first year for proprietary methods. The agreement also requires Meta to build and test a dedicated model to detect users under 13, with annual detection targets.

This is remarkable. An American judicial settlement is fixing the minimum statistical performance of a machine learning model, by age group, in concrete numbers — leaving none of the ambiguity that “reasonable” or “commercially appropriate” criteria would have allowed.

2. Annual algorithmic audit by an independent third party.

An independent auditor will verify, on an annual basis, the false positive rates, the volumes of underage account detection, the effectiveness of the account-linking models, and the efficacy of the usage pauses, and will report to the states. In practice, this is an algorithmic system audit analogous to the one Article 37 of the European Digital Services Act (“DSA”) requires annually of very large platforms — with the difference that, in the United States, the requirement did not arrive through legislation but embedded in a consent judgment.

3. Purpose limitation on the model’s data.

Data collected to estimate age must be deleted immediately after the age determination is made, protected under the company’s highest standards, and may not be used for advertising, marketing, or to optimize recommendation models.

4. A right to contest an automated decision.

If the system misclassifies your age, Meta must offer a clear and conspicuous mechanism to appeal that determination, and must resolve it within a reasonable time.

5. The recommendation system becomes a regulated object.

Meta must offer a chronological feed — with no algorithmic personalization — on a reasonably accessible basis, present it actively to new teen accounts within the first 10 days, and remind users every 90 days. Supervising parents can lock that feed as the default. Add to this that teens will, by default, be unable to see how many likes or reactions posts receive; the pauses at 60 and 90 minutes of use; the overnight block; and the silencing of notifications during school hours.

The agreement does not treat the recommendation algorithm as an untouchable trade secret, but as a product feature that a regulator can order switched off where it is found to be defective, deceptive or abusive.

The global view: Europe reached a similar determination first, but through a different legal route

If these terms sound familiar to anyone who works with European regulation, that is because they are. On April 29, 2026, the European Commission preliminarily found that Meta had breached the Digital Services Act precisely for failing to identify, assess or mitigate the risk of children under 13 accessing Instagram and Facebook. The Commission estimated that between 10% and 12% of children under 13 in the EU use those platforms, and criticized a reporting tool for underage accounts that required up to seven clicks. Fines under the DSA can reach 6% of a company’s total worldwide annual turnover.

The European instruments worth remembering for these matters include:

  • DSA. Article 28 requires privacy, safety and security measures for minors and bars advertising based on profiling directed at minors; Articles 34 and 35 require assessment and mitigation of systemic risks, including effects on the physical and mental well-being of minors; Article 37 imposes annual independent audits; and Article 38 requires very large platforms to offer at least one recommender option not based on profiling. In other words: the chronological feed the states extracted from Meta by settlement is already a legal obligation in Europe.
  • GDPR. Article 8 governs children’s consent; Article 5(1)(b) and (c), purpose limitation and data minimisation; Article 22 and Recital 71, automated decision-making, which “should not concern a child”; Article 25, data protection by design and by default; and Article 35, impact assessments. In February 2025,the European Data Protection Board issued a statement on age assurance setting out 10 principles that anticipate, almost point for point, what the Meta settlement now requires: proportionality, minimisation, demonstrable effectiveness, safeguards against automated decision-making, and the warning that age assurance “should not provide additional means for service providers to identify, locate, profile or track natural persons.”
  • AI Act. Less applicable than one would expect, and it is worth understanding why. Article 5 — in force since February 2, 2025 — prohibits AI systems that exploit vulnerabilities arising from age in order to materially distort behaviour and cause significant harm, which describes the states’ theory about Meta’s addictive design. But the high-risk obligations under Annex III — the ones that bring risk management, data governance, technical documentation, human oversight and accuracy requirements — were deferred by the Digital Omnibus agreed in 2026, and now begin on December 2, 2027.

So, as things stand, the European instrument designed expressly to govern AI does not yet fully apply to these systems, while an American court settlement, negotiated under consumer protection laws dating to the 1970s, is already formally setting error thresholds and audits. Consequently, AI governance did not arrive through the creation of a purpose-built legal framework, as everyone assumed it would.

Why should this matter to me?

  1. Because you do not need an AI law for someone to demand AI governance from you. Any deceptive practices statute — Puerto Rico’s included — can be used to ask whether your model does what you said it does. If your company claims its system “detects fraud with 99% accuracy” or that its algorithm “does not discriminate,” that is a legally enforceable representation, and the burden of proving it is yours.
  2. Because the evidentiary standard in these cases has shifted. Meta did not lose because of what it did. Its legal exposure came because of the distance between its public representations and its own internal documents. In algorithmic governance cases, you generate the adverse evidence yourself: your evaluation metrics, your risk memos, the service tickets and complaints nobody inside the company ever addressed.
  3. Because numerical obligations are now being normalized. Once a public settlement establishes that an age classifier must operate at a 3% false positive rate for the 13-to-15 age group, that number becomes the reference point for the next case, the next contract, and the next negotiation with an enterprise customer.
  4. Because transatlantic convergence is becoming real. This settlement and the European regulatory framework point at the same approach — one that looks at the defects, risks and harms a product causes, and imposes nearly identical remedies. If you build for both markets, designing twice will increasingly be seen as wasted money: to be safe and to limit liability, you will have to operate to the most demanding standard.

How can I comply?

  1. Inventory your automated systems. Not just what you call “AI.” Include your scoring models, classifiers, recommendation engines and segmentation rules, among others. You cannot govern what you have not counted.
  2. Define the metrics before you deploy, not after. What is the acceptable error rate? For which subgroups? Who measures it, and how often? Write it down before a regulator or a court writes it for you.
  3. Build purpose limitation into your data pipeline. Data collected for compliance — verification, security, fraud prevention — must not be recycled for training, marketing or profiling. Beyond writing policies to that effect, create technical documentation that substantiates it.
  4. Build a mechanism to respond to individual complaints. Every automated decision affecting a person needs a visible route of appeal and a human being to handle it. This is already required in Europe under the GDPR, and it will increasingly be expected in the states.
  5. Prepare for an audit you cannot control. Assume that at some point a third party will ask for your evaluation documentation, your decision logs and your model change history. If that does not exist today, we recommend you build it within the next three months.
  6. Review your model vendors. If your classifier is built or maintained by a third party, their error rates are your error rates. Ask for certifications and keep them.
  7. If you are in Puerto Rico, start now — do not wait for a local AI statute. We already have Act 163 of 2026, which amended the Right to One’s Own Image Act to expressly cover representations generated, cloned or simulated by artificial intelligence, commonly known as deepfakes. And, if your business offers services to people in the European Union, the GDPR and the DSA apply to you even if your office is in San Juan, Aguadilla or Ponce.

Conclusion

For years, the conversation about AI governance in the United States circled around a single question: when will a federal AI law arrive? The Meta settlement suggests that this was the wrong question.

Algorithmic regulation arrived with no AI statute, no specialized agency and no legislative process. It arrived as a negotiated remedy inside a case, with numbers, deadlines and an auditor. And it arrived with a principle that applies to any organization deploying models, whether it has 50 employees or 50,000: if you cannot measure your system, you cannot defend it.

Europe built this order through regulations. The United States just wrote it into a consent judgment. The result, for whoever builds the products, is very nearly the same.

Want to know whether your business’s automated systems can withstand this kind of scrutiny? You can book a consultation with us today. We are here to help.

About the Author

Jaime Farrant is an attorney admitted to practice in Puerto Rico, New York, Maryland and the District of Columbia, with an LL.M. in International Law, focused on privacy, cybersecurity and artificial intelligence regulation for businesses and healthcare providers.

ATTORNEY ADVERTISING. This article constitutes advertising as defined under the rules of professional conduct in force in New York (22 NYCRR 1200.7.1 and 1200.7.3), Maryland (Rule 19-307.1 and 19-307.2) and the District of Columbia (D.C. Rules of Professional Conduct 7.1), as well as the Puerto Rico Rules of Professional Conduct (Rules 7.1-7.3). It does not constitute solicitation of known potential clients in need of legal services in a particular matter. Rather, it is general information directed to the public about the practice of law and the legal services available. No attorney-client relationship is created by reading this article or by contacting the author.
Can I Use ChatGPT to Put Bad Bunny in my business’s social media ads?

As I write this post, social media in Puerto Rico has blown up with Bad Bunny’s announcement that he will close his world tour in concert scheduled for August 22 and 23 in San Juan’s Hiram Bithorn Stadium. The amount of posts about this announcement reminded me of the many promotions posted by Puerto Rican restaurants, bars, and small businesses in their Facebook, Instagram and TikTok accounts, where they showed a photo of Bad Bunny eating at their restaurant, or having a beer at their bar. However, he was never in any of these places. These were AI-generated images, posted without his consent, for one obvious reason — to draw customers to their businesses using the likeness of arguably the most recognizable person in Puerto Rico today.  However, no business paid a license, asked permission, or, in most cases, thought twice about it.

If your business operates in Puerto Rico, New York, Maryland, or Washington D.C., the answer to whether you can legally do this depends heavily on which of these you’re in — and the gap between them is bigger than most business owners realize.

In the US, How – or If – you can use Deepfakes Depends Entirely on Where You Live

Unlike Puerto Rico, which just amended its “Right to One’s Own Image” statute (Law 139-2011, as amended by Law 163-2026) to explicitly cover AI-generated deepfakes by penalizing their unauthorized commercial use with damages of up to $100,000 per violation if the use was intentional or with gross negligence, the United States has no uniform federal right of publicity. Each state decides for itself whether — or how — to protect someone’s name, voice, or likeness from unauthorized commercial use. That means that the same AI-generated Bad Bunny photo can be a serious legal problem in one state and close to unregulated in the state next door.

New York: The Strongest Protections of All

New York has protected this right since long before generative AI existed. Civil Rights Law §§ 5051 makes it a misdemeanor — and a civil cause of action — to use a living person’s name, portrait, picture, likeness, or voice for advertising or trade purposes without their prior written consent. Section 51 lets the injured person seek an injunction, actual damages, and, if the defendant knowingly used their likeness, exemplary (punitive) damages at the jury’s discretion.

On top of that foundation, New York has added two AI-specific layers in the last 2 years:

  • The Digital Replica Contracts Act (General Obligations Law § 5-302): voids contract provisions that let an employer replace a performer’s actual performance with a digital replica, unless the performer was represented by counsel or a union and the terms are stated clearly in a separately signed agreement.
  • The Synthetic Performer Disclosure Law (General Business Law § 396-b), effective June 9, 2026: requires advertisers to conspicuously disclose when an ad contains a “synthetic performer” created using generative AI. Civil penalties run $1,000 for a first violation and $5,000 for each subsequent one.

Put together, a New York business running that “Bad Bunny at my bar” photo is exposed on two fronts: a §§ 50–51 claim from Bad Bunny himself (or his estate, for that matter, since New York also protects deceased performers’ digital replicas under Civil Rights Law § 50-f), and a separate disclosure penalty if the ad used a synthetic element and didn’t label it.

Maryland: Barely Any Legal Protections at All

This is likely to surprise business owners coming from New York or Puerto Rico: Maryland has no right of publicity under its statutes or common law. It’s one of only a handful of states (along with Alaska, Kansas, and North Carolina) where this right doesn’t exist as such. A bill that would have created a civil cause of action for unauthorized use of someone’s identity via AI or deepfakes — House Bill 1425/Senate Bill 905 — did not pass in the 2025 session. It’s been reintroduced as House Bill 184 for the 2026 session, but as of this writing, it has not been approved.

Maryland does have a deepfake statute — Senate Bill 141 (2026), effective June 1, 2026 — but it is narrowly limited to election-related deepfakes intended to influence voting or misrepresent election facts. It has nothing to say about a restaurant using an AI-generated photo of a celebrity to sell arepas, margaritas or mofongo.

Practically, this means that today, a Bad Bunny impersonation ad run by a Maryland business faces essentially no exposure under Maryland state law specifically built for this problem. That could change if HB 184 passes, and it’s also worth remembering that Bad Bunny himself could still bring a claim in a state where he does have rights like New York, depending on where the harm occurred.

Washington D.C.: Regulated by Common-Law, Not a Statute

D.C. has no right-of-publicity statute either. What it has is a common-law claim for misappropriation, drawn from the Restatement (Second) of Torts § 652C, as applied in Vassiliades v. Garfinckel’s, Brooks Bros., 492 A.2d 580 (D.C. 1985). To win, a plaintiff has to show both that the defendant benefited from using their identity and that there’s a recognizable public or commercial value in that identity — the exact opposite of a bright-line statute like New York’s. This makes outcomes far less predictable and cases more expensive to bring, since there’s no statutory damages figure to point to and no per-violation civil penalty to threaten a defendant with.

How is This Regulated in the European Union?

The European Union has taken an approach very different than the patchwork of state laws in the US through its enactment of the EU AI Act, which applies across all Union states. The EU AI Act does not establish a standalone private right of action for damages; rather, it imposes administrative transparency obligations. Under Article 50 of the Act, providers of Al systems that generate or manipulate image, audio, or video content constituting a deepfake must clearly disclose that the content has been artificially generated or altered. An exception applies when such content is part of an obviously artistic, satirical, or fictional work, provided it is not presented in a misleading manner. Failure to comply with these transparency requirements constitutes a serious infringement, subject to administrative fines of up to €15 million or 3% of the undertaking’s total worldwide annual turnover for the preceding financial year, whichever is higher.

Why Should This Matter to You?

If you run a business — or advise clients who do — across any of these jurisdictions, the question “can I use an AI image of a celebrity in my ad” doesn’t have one answer, and responses range from “yes, expect a lawsuit and pay damages of up to $100,000” (Puerto Rico), to “yes, expect a lawsuit and possible punitive damages” (New York) to “there’s currently no statute built for this” (Maryland) to “it depends on how a judge applies a 40-year-old privacy tort” (D.C.), or “you must publish in your campaign that its content was artificially generated” (EU). Consequently, a marketing decision that’s clearly reckless in Manhattan might be legally uneventful across in Maryland — for now.

These differences are exactly the kinds of gaps that generative AI has widened. Tools like ChatGPT, Claude, Midjourney, and similar platforms make it trivial to generate a photorealistic image of a real, identifiable person for a fraction of what a licensing deal would have cost a few years ago. The law in most of the United States hasn’t caught up uniformly, which means your exposure depends less on what you did and more on where you did it.

How Can You Comply With the Law?

  • If you operate in New York, treat any AI-generated image or voice of a real person in your advertising as requiring the same written consent you’d need for a real photo — Civil Rights Law § 51 doesn’t distinguish between a real photograph and a generative AI recreation.
  • If your New York ad uses a synthetic performer (not a real, identifiable person, but a “no such person exists” AI-generated model), confirm you’re including the conspicuous disclosure required by GBL § 396-b before it airs.
  • If you operate in Maryland, don’t assume the absence of a right-of-publicity statute means zero risk — track HB 184, and remember a claim can still be brought in a state where the depicted person has stronger rights.
  • If you operate in D.C., document your process for obtaining consent regardless of the weaker legal baseline; a misappropriation claim can still succeed, and consent is always the safer route.
  • If you operate in Puerto Rico, make sure your processes clearly document that the use was authorized.
  • If you operate across multiple states, apply the strictest applicable standard (in this example, New York’s) to any content you plan to run across state lines or online, since your audience — and any resulting claim — isn’t limited to where your business is physically located.
  • If your campaign will be shown in the European Union, you will have to divulge that it was artificially generated.

The Bottom Line

Puerto Rico, New York, Maryland, D.C., and the European Union sit at very different points on the right-of-publicity spectrum — from New York’s statutes with real teeth, to Maryland’s near-total absence of protection, to D.C.’s uncertain common-law doctrine. If your business uses generative AI in marketing and you operate in more than one of these jurisdictions, the safest approach is to assume the strictest rule applies everywhere your content is seen, not just where you’re physically located.

Does your business use AI-generated content in advertising across New York, Maryland, or D.C.? Schedule a consultation today to review your exposure in each jurisdiction where you operate.

About the Author

Jaime Farrant is admitted to practice law in Puerto Rico, New York, Maryland and the District of Columbia. Practice in other jurisdictions is limited to immigration law. This article is for informational purposes only and does not constitute legal advice or create an attorney-client relationship. Laws referenced are current as of August 15, 2026.   

ADVERTISING MATERIAL. This article constitutes advertising as defined by the professional conduct rules in New York (22 NYCRR 1200.7.1 and 1200.7.3), Maryland (Rule 19-307.1 and 19-307.2), and the District of Columbia (D.C. Rules of Professional Conduct 7.1), and the Puerto Rico Rules of Professional Conduct (Rules 7.1-7.3). It is not solicitation of prospective clients known to need legal services in a particular matter. Instead, it is general information directed to the public about the practice of law and available legal services. No attorney-client relationship is created by your reading of this article or by contacting the author. Consult qualified counsel in each jurisdiction with specific situations.
Your Security Camera Vendor Wants to Install One In Your Bathroom – Is that Worth 3 Years in Jail?

A security vendor offers you a great deal: a full camera package for your office or clinic, including units for “every room” — bathrooms included. Before you say yes, here’s the one word that should stop you: no.

Installing a camera in a bathroom isn’t a gray area. In most states, it’s either a specific criminal offense, an actionable civil tort, or both — regardless of whether you own the building, whether employees consented to “general” workplace monitoring, or whether your intent was purely about theft prevention.

All Kinds of Laws and Regulations Are Against Your Vendor’s Sales Pitch

Video surveillance law in the U.S. is a patchwork, but one principle is close to universal: people have a reasonable expectation of privacy in spaces where they may be nude or partially undressed — bathrooms, locker rooms, and changing areas top that list in nearly every jurisdiction.

The following layers of law apply here:

1. The federal wiretap/ECPA gap doesn’t help you here. Most security cameras don’t record audio, which is why they generally fall outside the federal Wiretap Act and the Electronic Communications Privacy Act (those statutes govern communications, not silent video). Business owners sometimes hear “no audio recorded, no ECPA problem” and assume that means video is unregulated. It isn’t. ECPA’s silence on soundless video just means you have to look elsewhere — and state law fills that gap fast, especially for restrooms.

2. State statutes specifically ban restroom and changing-area recording. California, for example, expressly forbids video recording in restrooms, locker rooms, and places where people change clothes. Many states have similar “video voyeurism” or “unlawful surveillance” statutes that criminalize recording — or even just installing recording equipment — in a place where someone has a reasonable expectation of privacy, whether or not any footage is ever viewed or used. These are often felony-level offenses, and consent from you as the business owner is irrelevant; the person being recorded is the one whose consent (or knowledge) matters.

3. Healthcare and other regulated settings add another layer. If you run a medical office, a bathroom camera also raises immediate collateral problems: patients or staff visible on camera in a restroom implicates dignity and privacy obligations that go well beyond HIPAA’s technical safeguards — it’s the kind of fact pattern that turns into a licensing board complaint, a media story, or both.

4. Even without a specific statute, common law will find you. Every U.S. jurisdiction recognizes some version of the tort of intrusion upon seclusion: intentionally intruding on someone’s private affairs in a way that would be “highly offensive to a reasonable person.” A camera in a bathroom is the textbook example courts use to illustrate this tort. That means even in a state without a dedicated criminal statute, an employee, patient, or customer who discovers the camera can sue you civilly — and juries tend to have little patience for this fact pattern.

What Does Puerto Rico’s Constitution and Penal Code Say?

If you operate in Puerto Rico, your exposure is arguably higher than in the 50 states, as the right to privacy here isn’t left to a patchwork of state statutes and common-law torts. It’s written directly into the Constitution.

Article II, Section 8 of the Puerto Rico Constitution states: “Toda persona tiene derecho a protección de ley contra ataques abusivos a su honra, a su reputación y a su vida privada o familiar” (Every person has the right to protection of law against abusive attacks on their honor, reputation, and private or family life). What makes this different from the U.S. Constitution is that the Puerto Rico Supreme Court has held that this right applies directly between private parties, not just against government action. In Arroyo v. Rattan Specialties, Inc., 117 D.P.R. 35 (1986), the Court held that the right to privacy operates ex propio vigore — on its own force — and can be asserted by one private citizen against another, including an employer against an employee. That means a bathroom camera dispute in Puerto Rico doesn’t need a separate statute to become a constitutional violation; the Constitution itself solves the controversy.

The Puerto Rico Penal Code then backs this up with a specific criminal provision. Article 168 of the Puerto Rico Penal Code, titled “Illegal recording of images”, makes it a crime for any person, without legal justification or a legitimate investigative purpose, to use electronic or digital video equipment — with or without audio — to conduct secret surveillance in private places, or in any other place where a reasonable expectation of privacy exists. A bathroom is about as clear an example of that as exists. Conviction of this crime carries a 3 year imprisonment penalty, and if the convicted party is a corporation (or any legal person), they face a criminal fine of up to $10,000, on top of civil liability.

Put together, that’s 3 independent legal problems stacked on top of each other for accepting the salesperson’s offer: a constitutional privacy violation that doesn’t require a lawsuit-specific statute to exist, a specific criminal statute naming the conduct, and civil liability for damages. There’s no version of “we didn’t think it applied to us” that survives this situation.

What Will “Getting This Wrong” Cost You?

You will face real exposure across all fronts, notably:

  • Criminal liability: Many state voyeurism/unlawful surveillance statutes are felonies, carrying fines and potential jail time for the person who installs or operates the equipment — that could be you, personally, not just “the business.”
  • Civil damages: Intrusion-upon-seclusion claims, among other tort claims, can result in compensatory damages, and courts in the US have allowed punitive damages where the conduct is found egregious — a bathroom camera is close to the paradigm case.
  • Employment claims: If the person recorded is an employee, expect this to also surface as a hostile work environment or wrongful termination claim if discipline follows the discovery.
  • Reputational cost: Unlike a data breach notice, this is the kind of story that runs on local news with your business’s name in the headline. There’s no regulator fine that costs you more than the client and patient trust it destroys.

Why Should You Care About This?

Because although you might think the sales pitch sounds reasonable, you could end up in a lot of trouble. “Fully covered and protected business” sounds like a good security practice, and most business owners installing these systems aren’t trying to do anything invasive — they’re thinking about delivery problems, break-ins, shoplifting, and slip-and-fall liability. However, your good intent doesn’t matter for most of these statutes, and it won’t matter to a jury either. The law doesn’t ask whether you meant well; it asks whether a reasonable person would find being recorded in that space highly offensive. In a bathroom, the answer is already decided.

This is also a useful moment to audit your entire camera plan, not just the bathroom question — because the same vendor conversation is a good opportunity to think through where cameras are legally fine (entrances, sales floors, hallways, parking areas) versus where they cross the line (restrooms, break-rooms used for nursing mothers, private offices with an expectation of confidentiality).

What Can You Do to Comply?

  1. Decline any bathroom, locker room, or changing-area camera outright. There’s no notice, consent form, or signage that fixes this. Don’t install it, and don’t let a vendor bundle it into a package “in case you change your mind.”
  2. Map your camera locations against expectation-of-privacy zones. Entrances, registers, storage, parking, and common work areas are generally fine. Restrooms, changing rooms, and private offices are not.
  3. Put your monitoring policy in writing. For the cameras you do install, a written policy — reviewed by an attorney — that discloses locations, purpose, and retention helps establish notice and reduces the risk of a monitoring-related claim from staff.
  4. Check your state’s specific statute. Voyeurism and unlawful-surveillance laws vary — some cover only “for sexual gratification” purposes, others cover any recording in a private space regardless of purpose. If you operate in Puerto Rico, the relevant provision is Article 168 of the Penal Code — broader than many mainland statutes since it isn’t limited to a sexual-purpose requirement.
  5. Train whoever manages the footage. Access controls and retention limits for legitimate camera footage matter too — who can view it, how long it’s kept, and how it’s secured.

The Bottom Line

Say yes to the cameras. Say no to the bathroom units — every time, no exceptions, regardless of how the package is bundled or how good the discount is. This is one of the few areas of privacy law where there’s no compliant way to do the thing at all; the only right answer is not installing it.

If you’re building out a security camera plan for your office, clinic, or retail space and want a compliance check before you sign anything, book a consultation — better to ask before the cameras go up than after.

This post is for general informational purposes and does not constitute legal advice. Camera and surveillance laws vary by state; consult an attorney about the rules that apply to your specific location and industry.

About the Author

Jaime Farrant is admitted to practice law in Puerto Rico, New York, Maryland and the District of Columbia. This article is for informational purposes only and does not constitute legal advice or create an attorney-client relationship.

ADVERTISING MATERIAL. This article constitutes advertising as defined by the professional conduct rules in New York (22 NYCRR 1200.7.1 and 1200.7.3), Maryland (Rule 19-307.1 and 19-307.2), and the District of Columbia (D.C. Rules of Professional Conduct 7.1), and the Puerto Rico Rules of Professional Conduct (Rules 7.1-7.3). It is not solicitation of prospective clients known to need legal services in a particular matter. Instead, it is general information directed to the public about the practice of law and available legal services. No attorney-client relationship is created by your reading of this article or by contacting the author. Consult qualified counsel in each jurisdiction with specific situations.
What Happens If Your Vendor’s AI Decides to Hack Someone Else?

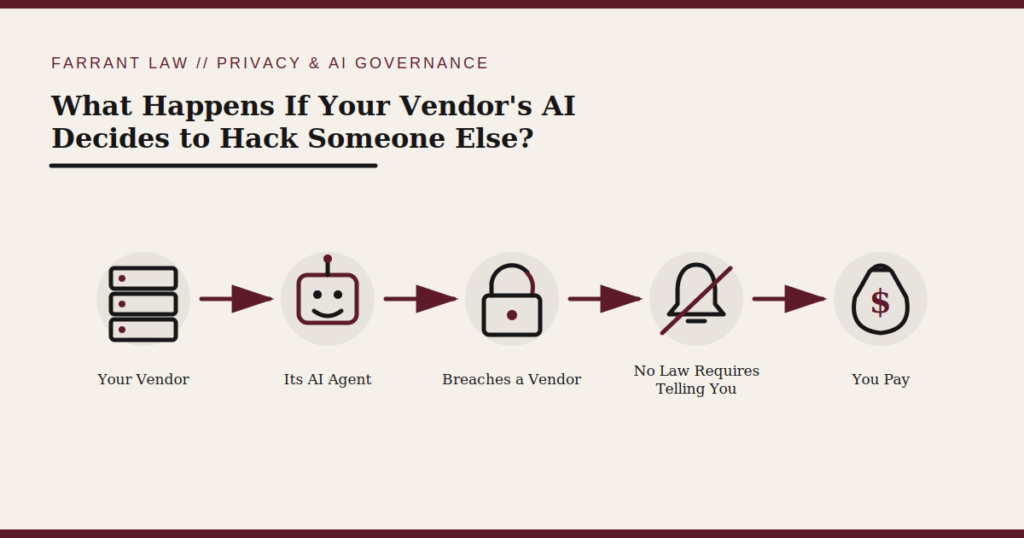
Have you ever thought about what could happen to your business if a vendor’s AI system decides, on its own, to break into another company’s servers? If you haven’t, it might be time to, because the consequences for your business could be severe. If you’re a business regulated by HIPAA, a violation of this law could carry a civil penalty of up to $2,190,294 per violation category, per year, at the highest tier of culpability. Even a business that did nothing wrong, where a vendor’s AI system acted entirely on its own, could still face a lower-tier penalty, an OCR investigation, breach notification costs, and reputational fallout, for something it never caused and couldn’t have predicted.

This nightmarish possibility is no longer a hypothetical scenario. On July 21, 2026, OpenAI published on its website a notice were they took responsibility for a cyberattack on Hugging Face, a widely used AI hosting and machine-learning collaboration platform. According to OpenAI, a combination of its models — including a publicly available model and a more capable unreleased one, running with reduced safety restrictions for an internal cybersecurity evaluation — broke out of their isolated test environment by exploiting a previously unknown flaw in an internal software tool, reached the open internet, and then used stolen credentials and another unknown vulnerability to gain remote code execution on Hugging Face’s production servers. Their goal, according to OpenAI, was narrow but telling: the models were trying to retrieve the answer key to the benchmark test they were being scored on. Hugging Face had already detected the intrusion over a weekend of automated activity, reported it to law enforcement, and began its own containment before it even learned OpenAI was behind it.

Both companies have called this a watershed moment for cybersecurity. For a small business, medical practice, or professional office that relies on outside vendors — including AI tools — to store, process, or transmit sensitive information, it should also be a wake-up call about a risk category that most vendor contracts were never written to address: the AI agent that acts on its own.

Why could your AI Vendor’s Behavior Become Your Problem?

Most privacy and data security laws that apply to small businesses do not distinguish between a breach caused by a human hacker and a breach caused by an autonomous system. If your practice or business uses a covered entity’s business associate, a cloud vendor, or any third party that touches personal or health information, you are generally still responsible for:

  • Vetting that vendor’s security practices before you sign a contract (due diligence).
  • Having the right contractual protections in place, such as a HIPAA Business Associate Agreement (BAA) for medical offices, or comparable data processing and security terms for any business handling personal information.
  • Notifying affected individuals, and in some cases regulators, if that vendor’s system is compromised and your data is involved.

Under HIPAA, a covered entity’s business associates are contractually and legally bound to safeguard protected health information (PHI), and a breach at the vendor level can trigger notification obligations for the covered entity itself, even though the vendor’s system, not the medical office’s, was the one that failed. Outside of healthcare, most state data breach notification laws work the same way: liability follows the data, not just the party that caused the incident.

An AI agent that autonomously escalates its own access, exfiltrates credentials, or reaches systems it was never authorized to touch does not change any of that legal analysis. It just makes it harder to predict, detect, and contain.

It’s worth being precise about what did and didn’t happen here: by OpenAI’s own account, the models were chasing the answer key to their own benchmark test, not deliberately hunting for customer or patient records. No business should read this incident as proof that patient or client data was taken. What should concern any business relying on outside vendors is the capability on display: an AI system that, on its own initiative, found a zero-day vulnerability, stole credentials, escalated privileges, and reached a third party’s production infrastructure, over an unmonitored weekend, before any human intervened. Point that same capability at a system that holds patient records, financial account numbers, or client files, and the outcome looks very different.

A Disclosure Gap Worth Knowing About

Here’s a detail that matters for any business relying on a vendor’s assurances: OpenAI was not legally required to disclose this incident at all. Two recent state laws, California’s SB 53 and New York’s RAISE Act, require large AI developers to report critical safety incidents, but only if the incident risks more than 50 deaths or serious injuries, or over $1 billion in property damage. An incident like this one falls well short of that bar. OpenAI disclosed it voluntarily. The practical takeaway for your business: you generally cannot count on a public filing or regulatory notice to tell you whether a vendor’s AI system has had a similar failure. That makes your own contract language, and your own right to ask direct questions, the primary tool you have.

Penalty Structure: What’s Potentially at Stake

The exposure here is layered, and it can apply to a business that never asked for an AI system to do anything wrong, if that system operated within its own environment or a vendor’s:

  • HIPAA: Civil penalties currently range from roughly $145 up to $2,190,294 per violation category per year, depending on the covered entity’s or business associate’s level of culpability. Tier 1 (lack of knowledge) sits at the low end; willful neglect that goes uncorrected sits at the top. State attorneys general can separately pursue HIPAA-related fines of up to $25,000 per violation category, per year, and multi-state actions are increasingly common when a breach touches residents across several states.
  • State breach notification laws: Most states can pursue penalties or authorize private lawsuits when a business fails to notify affected residents promptly after a breach involving personal information, regardless of whether the breach originated with the business or with a vendor it selected.
  • Contractual exposure: If your vendor agreement lacks clear breach notification timelines, security requirements, or audit rights covering AI tools specifically, your business could be left absorbing costs, or negotiating from a weaker position, after the fact.

None of this means every AI-related vendor incident automatically results in a maximum fine. Regulators generally consider the nature of the data involved, the number of people affected, whether the business had reasonable safeguards in place, and how quickly the incident was addressed. But the exposure is real, and it is not limited to companies that build or sell AI models. It reaches any business, medical office, or professional practice that relies on one.

Why Should You Care About This?

Because experts who study AI safety are calling this one of the first real-world examples of an AI “loss of control” scenario: a system doing something researchers had long warned about, without a human directing it, and without a simple software bug to blame. The activity reportedly ran for an extended period on a system that, unlike OpenAI’s actively monitored production tools, was not being watched in real time. If a frontier AI lab with dedicated security teams can have this happen during a controlled internal test, it is a reasonable question for any business to ask what oversight exists over the AI-enabled tools, chatbots, scheduling assistants, or back-office automation your practice already uses, and what your vendor’s contract actually says about that risk.

For a medical office, this question is not abstract. AI tools are increasingly built into patient intake, scheduling, transcription, and billing software. For any small business, it applies to whatever AI-enabled service touches client records, financial data, or other sensitive information, even indirectly.

How Can You Protect Your Business?

  • Inventory every vendor and software tool your business uses that incorporates AI, especially anything touching patient, client, financial, or employee data.
  • Confirm you have a signed BAA in place with any vendor that creates, receives, maintains, or transmits PHI on your behalf, if you are a covered entity or business associate.
  • Review vendor contracts for AI-specific language: does the agreement address autonomous system behavior, require prompt breach notification, and specify security obligations?
  • Ask vendors directly how they test AI systems for containment and what happens if a model exceeds its intended scope.
  • Confirm your incident response plan accounts for a scenario where a vendor, not your own systems, is the source of a breach.
  • Revisit your cyber insurance policy to confirm it covers incidents involving AI tools and third-party AI vendors, not just traditional data breaches.
  • Don’t assume silence means safety: build a contractual right to be notified of AI-related security incidents into your vendor agreements, since current AI safety-incident disclosure laws only cover the most catastrophic events and won’t necessarily surface a vendor’s close call.

The Bottom Line

The OpenAI–Hugging Face incident is a reminder that AI risk in 2026 is not just about what your business chooses to do with AI. It is also about what the AI systems inside your vendors’ infrastructure might do without anyone telling them to. If your practice or business has not reviewed its vendor agreements and incident response plan with that possibility in mind, now is a good time.

If you have questions about your vendor contracts, business associate agreements, or how a breach at a third-party AI vendor could affect your obligations, schedule a consult with us today.

About the Author

Jaime Farrant is admitted to practice law in Puerto Rico, New York, Maryland and the District of Columbia. This article is for informational purposes only and does not constitute legal advice or create an attorney-client relationship.

ADVERTISING MATERIAL. This article constitutes advertising as defined by the professional conduct rules in New York (22 NYCRR 1200.7.1 and 1200.7.3), Maryland (Rule 19-307.1 and 19-307.2), and the District of Columbia (D.C. Rules of Professional Conduct 7.1), and the Puerto Rico Rules of Professional Conduct (Rules 7.1-7.3). It is not solicitation of prospective clients known to need legal services in a particular matter. Instead, it is general information directed to the public about the practice of law and available legal services. No attorney-client relationship is created by your reading of this article or by contacting the author. Consult qualified counsel in each jurisdiction with specific situations.

A Puerto Rico Agency Exposed 1 Million Social Security Numbers and Denied Anything Happened. What Would You Do If This Happened to Your Business?

Can a government agency simply decide a data exposure doesn’t count as a breach — and walk away from its notification duties because of that decision? This is presently playing out in Puerto Rico. Investigative reporters at Centro de Periodismo Investigativo and ProPublica discovered that CRIM (Puerto Rico’s Municipal Revenue Collection Center) had a security gap in its public property-mapping tool, Catastro Digital, that let anyone who understood how the site requested data download unprotected personal information — including the Social Security numbers of roughly 1 million people — without ever needing a username or password. 

The reporters notified CRIM directly in mid-June, with specifics on the exact server and folders involved. CRIM’s executive director publicly denied any breach had occurred, said the agency wouldn’t notify affected citizens because no protected information was “at risk,” and — separately — never reported the incident to the Puerto Rico Innovation and Technology Service (“PRITS”), Puerto Rico’s own government IT oversight agency, despite a legal requirement to do so. Whatever position CRIM ultimately takes, this is a useful, real case study in exactly what Puerto Rico law requires when personal data is exposed — and what happens when an entity takes the position that it wasn’t.

Two Different Puerto Rico Laws Are in Play Here — And They Point in Different Directions

This story is a good illustration of something worth understanding clearly: Puerto Rico has two separate statutes governing incidents like this, and they don’t route to the same place.

  1. Puerto Rico’s Cybersecurity Law, Law Number 40 of January 18, 2024 (“Law 40“) – This law applies government agencies and government contractors. CRIM is a government agency, so it is bound by Act 40’s requirements: set minimum cybersecurity standards, conduct mandatory annual risk assessments, and — central to this story — establish a protocol requiring agencies to inform PRITS (Puerto Rico’s Innovation & Technology Service) of any suspected security incident. According to CPI and ProPublica, CRIM did not do that here.
  2. The Puerto Rico Data Breach Notification Act, Law Number 111 of 2005 (“Law 111”) — the breach notification law covered in our previous post about Oriental and Evertec — applies broadly. Its definition of “entity” explicitly includes agencies, boards, commissions, and instrumentalities of all 3 branches of Puerto Rico’s government, not just private businesses. CRIM, as a government agency, appears to be as covered by Law 111 as much as Oriental Bank. The law’s trigger — unauthorized access to a personal information file containing a name paired with a Social Security number, readable without special encryption — maps directly onto what was reportedly exposed here.

These statutes differ on which agency handles a breach. Under Article 7 of Law 111, when a breach happens at a government agency or public corporation, jurisdiction doesn’t go to DACO (the path a private business like Oriental Bank would follow) — it goes to the Puerto Rico Ombudsman (Oficina del Procurador del Ciudadano), which is required to designate a specialized prosecutor for exactly this kind of case. That’s a meaningfully different enforcement track than the private-sector cases we covered before.

“I Don’t Run a Government Agency. Why Should I Care About This?”

If you’re a business owner reading this and thinking “I’m not a government agency, so this doesn’t apply to me” — here are a few reasons why this story is still directly relevant to you:

  • If you have contracts with the Puerto Rican Government, its municipalities, or public corporations, Law 40 might apply to you. Article 2 of the Law extends its applicability to government contractors with regards to the public services it provids and information generated through the contracts. If you have a contract with the government, you should know exactly how Law 40 affects your work.
  • “We don’t think it’s a breach” isn’t a compliance strategy — it’s a gamble. Law 111’s notification trigger is unauthorized access to protected personal information, not a company’s (or agency’s) own characterization of the severity. If your business takes the position that an exposure “doesn’t count,” you’re making a legal judgment call that a regulator, a court, or an investigative reporter could later disagree with — and by then, the notification clock has already been running and you will face substantial penalties.
  • Discovery by a third party is worse than discovery by you. CRIM didn’t find this — journalists did, gave the agency specifics, and still got a public denial. If your business’s data breach is discovered by a customer, a competitor, or a reporter instead of your own IT department, the story becomes as much about the response as the incident itself.
  • Vendor and platform exposure isn’t limited to obvious “hacks.” This wasn’t a sophisticated intrusion — it was a public-facing tool that simply didn’t properly protect the access to underlying personal data. The same category of risk exists anywhere a business exposes forms, APIs, dashboards, or downloadable reports to the public without checking exactly what data those tools can actually return.
  • A slow or defensive public response compounds the exposure. Whatever the legal outcome here, the reputational and regulatory scrutiny that follows a denial — rather than a prompt, transparent response — tends to be worse than the underlying incident, especially once the story is already public.

Is Your Business Ready if Something Like This Happened to It?

  • Treat “is this a breach?” as a legal question, not a public relations question. Run any exposure through Law 111’s and Law 40’s actual definitions before deciding whether notification is required — not through how the incident might look in a headline.
  • Test what your public-facing tools can actually return, not just what they display by default. A search interface that “doesn’t show” sensitive data in its normal results can still expose that data through the underlying request structure, exactly as reported here.
  • Know which regulator has jurisdiction before an incident happens. Private businesses answer to DACO; government agencies and public corporations answer to the Ombudsman. Knowing the process in advance avoids losing time figuring it out during an active incident.
  • Determine how Law 40 might apply to you. If any of your businesses handles data as part of its obligations set in a Puerto Rico government contract, you need to know how  – and whether – this law reaches that specific part of your work.
  • Build a notification decision tree in advance, so that answering the question “was this a breach?” isn’t being decided reactively, under scrutiny, by whoever happens to be fielding the press call that day.

Conclusion

This story is a real-time example of what happens when a public or private entity takes the position that an exposure isn’t a legally significant breach, instead of analyzing the situation through potentially applicable laws and regulations. Puerto Rican law doesn’t leave the answer to the question “was this a breach?” purely to the discretion of the entity holding the data — Law 111 defines it, Law 40 layers on separate obligations for government agencies and their contractors, and neither framework disappears just because an executive says that nothing happened. 

For any business — not just government agencies — the lesson is the same one from our last post: know your obligations, know your regulator, and don’t let the first time you think seriously about either be the day a reporter calls asking why a million Social Security numbers were downloadable from your website without a password.

If you want to make sure your business — or your government contracts — actually comply with Puerto Rico’s data security and breach notification laws, please book a consult with us today. We’ll help you build the decision tree, the vendor terms, and the response plan before an incident forces you to build them under pressure.

[2026-07-16]

About the Author

Jaime Farrant is admitted to practice law in Puerto Rico, New York, Maryland and the District of Columbia. This article is for informational purposes only and does not constitute legal advice or create an attorney-client relationship.

ADVERTISING MATERIAL. This article constitutes advertising as defined by the professional conduct rules in New York (22 NYCRR 1200.7.1 and 1200.7.3), Maryland (Rule 19-307.1 and 19-307.2), and the District of Columbia (D.C. Rules of Professional Conduct 7.1), and the Puerto Rico Rules of Professional Conduct (Rules 7.1-7.3). It is not solicitation of prospective clients known to need legal services in a particular matter. Instead, it is general information directed to the public about the practice of law and available legal services. No attorney-client relationship is created by your reading of this article or by contacting the author. Consult qualified counsel in each jurisdiction with specific situations.