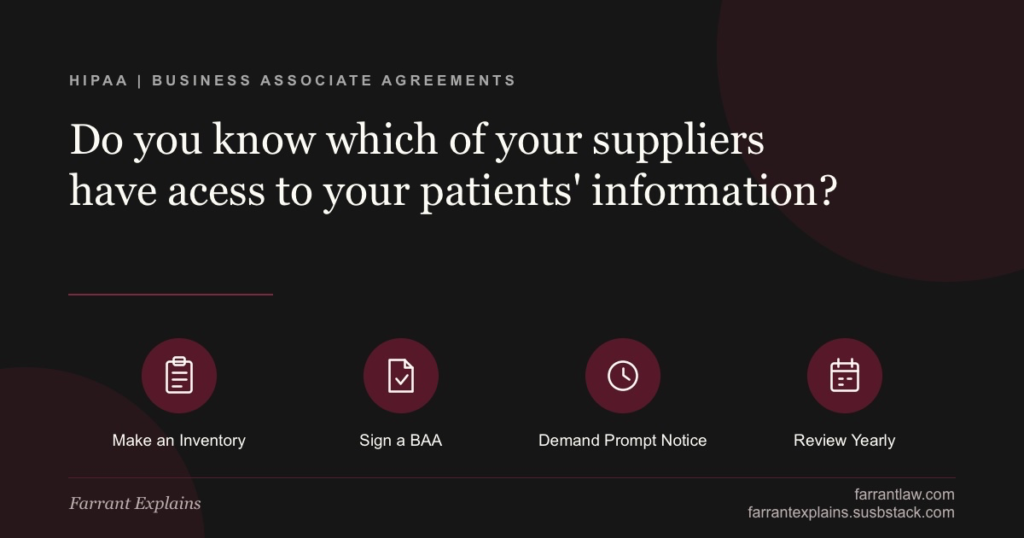
Do you know which of your vendors can access your patients’ information and whether you’ve signed contracts with them?
In April 2016, Raleigh Orthopaedic Clinic paid $750,000 to the Office for Civil Rights (“OCR”) within the U.S. Department of Health and Human Services (“HHS”). Why? The clinic had disclosed protected health information (“PHI”) to a service provider without first signing a Business Associate Agreement (“BAA”). They hired a vendor to digitize X-rays but allowed him to extract X-ray data without contractual safeguards.
That was the entire violation: the vendor had access to X-rays without a formal agreement.
If your medical practice uses billing companies, medical record services, cloud backup providers, IT consultants, or appointment scheduling tools, this applies to you. In this article, we’ll explain what a BAA is, who needs one, why signing it doesn’t eliminate your liability, and how Puerto Rico’s law affects your obligations.
What Is a Business Associate and Why Does the Law Require Contracts With Them?
A Business Associate is a person or entity that performs functions or services on behalf of a covered entity (like a medical practice) involving PHI. HHS rules state that activities like claims processing, billing, data analysis, practice management, legal/ accounting firms, consulting, or administrative services qualify as Business Associates.
The rule is straightforward: Under 45 C.F.R. § 164.502(e) and 45 C.F.R. § 164.504(e), covered entities may share PHI with Business Associates only after obtaining written guarantees that the vendor will protect the data. These guarantees are formalized in the BAA. At minimum, this contract must:
- Define permitted uses/disclosures of PHI and prohibit others.
- Mandate appropriate safeguards.
- Require breach/incident reporting.
- Obligate subcontractors to accept identical restrictions.
- Allow HHS audits and support patient rights (access, amendment, disclosure accounting).
- Specify data disposition post-contract.
Not all vendors require BAAs. HHS exceptions include:
- Disclosing PHI to another provider for treatment.
- Sending claims to insurers for payment.
- Postal services delivering mail.
- Cleaning staff with incidental PHI access.
Obligations don’t end at signing. If your practice learns a vendor suffered a significant breach, you must take reasonable steps to mitigate or terminate the contract. If termination isn’t feasible, report the issue to HHS.
Vendor Liability Doesn’t Absolve Your Responsibility
Since Congress passed the HITECH Act (2009) and OCR’s 2013 Final Rule, Business Associates bear direct liability for certain HIPAA requirements, including:
- Compliance with the Security Rule.
- Breach notification to covered entities.
- Limiting disclosures to authorized uses.
- Signing BAAs with their own subcontractors.
How does OCR handle breaches involving vendors?
- 2016: Catholic Health Care Services (Archdiocese of Philadelphia) paid $650,000 after an unencrypted iPhone with 412 residents’ data was stolen. OCR cited inadequate risk analysis.
- 2018: Pagosa Springs Medical Center (Colorado) paid $111,400 because a former employee retained ePHI access post-termination.
- 2025: Comstar LLC (ambulance billing company) settled for $75,000 after a ransomware attack exposed the data of 585,621 patients.
Why Should This Matter to You?
1. No Contract = Automatic Violation
You don’t need a breach for OCR to intervene. Lack of a BAA alone violates HIPAA.
2. Vendor Breaches Become Your Notification Problem
If a Business Associate suffers a breach, you’re responsible for notifying affected patients.
3. Puerto Rico’s Local Law Applies
Law 111-2005 treats HIPAA-protected data as personally identifiable information. It requires reporting breaches to the Department of Consumer Affairs (“DACO”) within 10 days, with public notice within 24 hours. This applies even to password-only unprotected data.
→ Scenario: If your vendor delays reporting a breach for 2 weeks, you could violate Puerto Rico law despite HIPAA’s longer timeline.
4. Include Vendors in Risk Assessments
Without knowing what data your vendors hold, you can’t accurately document required HIPAA risk analyses as we discussed previously here.
How Can You Comply with the law?
Though this is a time-intensive project, you can start with these steps:
- Create a Vendor Inventory – List everyone who accesses patient data.
- Categorize Vendors – Separate those requiring BAAs from exemptions.
- Review Existing Contracts – Confirm BAAs were signed.
- Audit Contract Clauses – Ensure breach protocols and data disposition terms exist.
- Negotiate Notification Deadlines – Require immediate incident reporting.
- Demand Subcontractor Transparency – Ask where subcontractors store data and their sub-subcontractors.
- Schedule Annual Reviews
Conclusion
While a BAA may seem like a routine contract, OCR views it as the gatekeeper of patient data. Penalties begin when that gate opens without authorization.
Ask yourself: If OCR audited your office today, could you produce a list of every vendor accessing patient data—and their signed BAAs—within 24 hours?
If your answer is “no” or “I’m unsure,” start this process immediately.
Are you interested in verifying your vendor contracts comply with HIPAA or Puerto Rico law? Schedule a consultation today. We’re here to help.