In a recent article, we spoke with the directors of Seabase and explained their interest in exploring the installation of undersea AI data centers in Puerto Rico’s waters, and how the Joint Regulation and current laws could apply to a novel project like this one. However, that analysis could change significantly if the Planning and Permits Code, recently approved by the Puerto Rico Senate, becomes law. This Code is an 868-page bill that rewrites how projects will be approved in Puerto Rico.
A review of this bill reveals that it does not mention data centers even once. As a result, any proposal similar to Seabase’s would be evaluated under general rules, and the outcome would depend on the route it takes. In this article, Farrant Explains how this Code, if it becomes law as written, could treat such proposals.
What Is This Code?
The Code approved by the Senate on October 13, 2026 was a “substitute” version that replaced Senate Bills 1173 and 1183. It brings together, in a single Code, rules scattered across more than 50 laws. It also proposes creating the “Central Permits Office,” attached to the Department of Economic Development and Commerce (“DDEC”), as the entity that would receive and consider permit applications, along with an Adjudicative Board. In addition, in Articles 7.02 and 7.03, it orders the Planning and Urban Development Board to draft the “Unified Planning and Permits Regulation of Puerto Rico” (the “Unified Regulation”), which would replace the Joint Regulation. As of October 13, La Fortaleza had not decided whether it would sign the bill if the House of Representatives approves it, and the measure currently faces opposition from multiple sectors, including environmental, scientific, and planning groups.
Which Route Would Be Used to Evaluate This Project?
It is hard to imagine an undersea data center as a permitted use that would be approved “ministerially,” that is, automatically. For projects like this one, the Code keeps the Site Consultation (Consulta de Ubicación), which it says applies when projects propose “a use that is not ministerially permitted or that requires a change in planning on undeveloped land, or when so required by this Code or by the Unified Regulation under previously established objective criteria for projects that, by their nature, complexity, location, or potential impacts, require a greater degree of analysis” (Art. 12.24, our translation). That same article provides that the evaluation and adjudication process “may include holding a public hearing,” meaning it is discretionary, just as it currently is under the Joint Regulation.
With that in mind, let’s look at the routes this project could take under this Code, if it becomes law as written.
Route 1: Site Consultation and Environmental Review
If the project takes this course, here is what it would mean for the public:
- Notice. A posted filing sign, certified mail to adjoining property owners, and notice to the municipality and to any municipalities within 200 meters (Arts. 12.34, 12.50, and 12.51). Those municipalities would have 15 days to submit recommendations, which are not binding. The sign must be installed “on the land or structure that is the subject of the application,” and if the land borders a body of water, the owner on the other side is also notified. This raises a question: since this project would be in the sea, where would the sign be posted, and who would be the adjoining property owner that receive the notice?
- Public hearing. The process “may include” a hearing, as established by the future Unified Regulation. Therefore, for now, it would be discretionary.
- Environmental review. The project would go through a categorical exclusion, an Environmental Assessment (EA), or an Environmental Impact Statement (DIA, for its Spanish acronym). Neither the exclusion nor the EA admits third-party intervention. The Code also presumes that an action meeting the applicable parameters does not produce a significant impact requiring a DIA. And even when a DIA is required, the Code requires publishing it for comments, but a public hearing would be held only “when applicable” (Arts. 12.36 to 12.39).
- Participation. The Code proposes creating a public registry of all applications, with access to copies of public documents. It also allows anyone with a legitimate interest to ask to be an intervening party (Art. 12.52). The specific mechanisms for intervening would be defined in the Unified Regulation.
Route 2: The Priority Track
The Code proposes creating “Priority Socioeconomic Impact Projects.” These could include, among others, energy generation, transmission, and distribution projects approved by the Energy Bureau, projects designated as strategic, and those designated by the governor. A committee made up of the DDEC, the Planning and Urban Development Board, and a designee of the governor would determine which projects are strategic. Art. 2.06(d) further provides that Priority Projects in Opportunity Zones under Act 60 would be considered strategic.
For these “priority” projects, the proposed process would be as follows:
- The application is filed directly with the Central Permits Office, even if a municipality has delegated authority.
- Agencies and municipalities would have 20 calendar days to issue recommendations. If they do not respond, it is understood that they have no recommendations or comments. The affected municipality must be formally consulted within 20 business days.
- For non-critical infrastructure, including strategic projects, the environmental determination would be issued within 10 calendar days after the recommendation period ends. Strategic projects can receive the same environmental treatment as critical projects established under PROMESA, which could be filed as a categorical exclusion with no additional requirements.
- Notice for these projects would only need to be given through a posted sign.
- The process for these projects displaces the Environmental Public Policy Act and the Uniform Administrative Procedure Act where they conflict.
- Judicial review must be filed within a jurisdictional period of 20 days, and the work cannot be halted unless a court expressly orders it to prevent irreparable harm (Art. 12.40(f)).
As of this writing, the version of the Code approved by the Senate does not say that a data center would be considered a Priority Socioeconomic Impact Project. The criteria for designating strategic projects would be set by the DDEC through regulation. However, any energy generation, transmission, and distribution proposal approved by the Energy Bureau would fall into this category. If the Code becomes law, it will be worth watching whether the energy component that the Energy Bureau approves for an AI data center would fall into this category.
Who Will Approve the Permits?
Based on our reading of the bill approved by the Senate, the Code would centralize permits in the central government. For example, permits in the maritime-terrestrial zone would move to the Central Permits Office (Art. 15.30). The Department of Natural and Environmental Resources (“DRNA”) appears to lose the authority to grant franchises and licenses over territorial waters, submerged lands, and the maritime-terrestrial zone, although it keeps its oversight and conservation functions. In port zones, the Central Office would issue the permit with a recommendation from the Ports Authority. However, we notice a gap here: the bill does not say who would authorize the use of submerged lands outside the maritime-terrestrial zone.
The Details Will Be Found in the Unified Regulation
Most of the pressing issues covered by this proposed Code, for example, when hearings will be held, what counts as a “significant impact,” and which works are excluded from environmental review, are not regulated in it. The Code provides that the Planning and Urban Development Board will prepare and adopt the Unified Regulation, whose main purpose is to “provide a uniform, integrated, and coherent body of rules covering all regulatory provisions related to the evaluation, adjudication, and review of applications for recommendations, consultations, permits, authorizations, licenses, and environmental compliance evaluations for the development or use of land and the operation of businesses in Puerto Rico” (Art. 7.02, our translation). Until it is approved, the Joint Regulation would remain in effect (Art. 16.04).
The Board has 60 days from the Code’s effective date to begin drafting the Regulation and 180 days to prepare it, and the regulation takes effect 30 days after it is filed. If these deadlines are followed, the Regulation would be approved in about 9 months.
The Code requires notices in Spanish and English about the adoption of the Regulation, a 60-day comment period, and between 1 and 3 mandatory public hearings (Art. 7.07). Afterward, partial amendments would require 30 days of comments, and hearings would be discretionary (Arts. 7.03 and 7.09). A challenge for procedural defects must be brought within 30 days of the regulation’s effective date and would not stay the regulation (Art. 7.10).
In Summary
What would change under this bill? Comparing it with the sections of the Joint Regulation we explained in our previous article, this is what would change in the Site Consultation process for a project like this one:
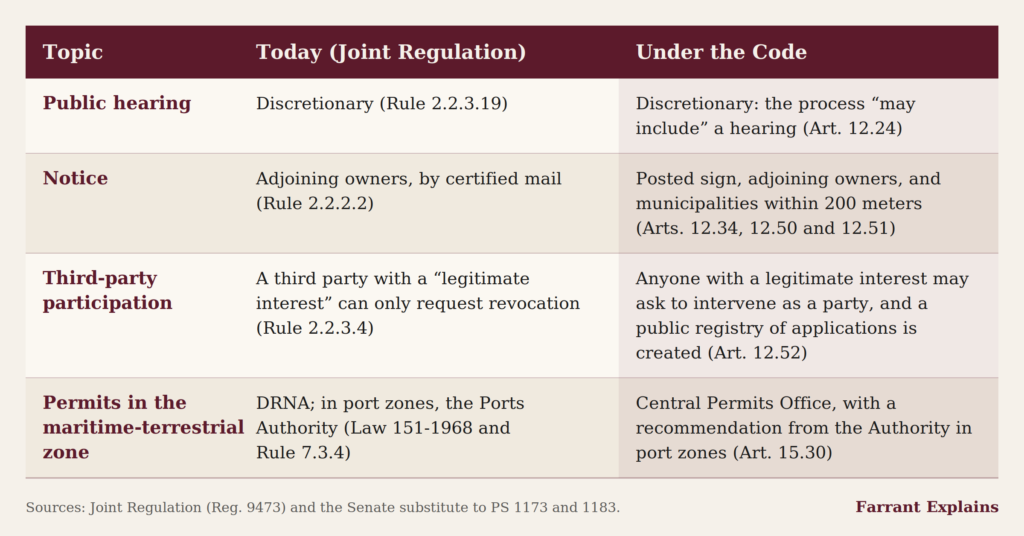
In summary, the Code improves current processes a little in terms of transparency: it offers a public registry of applications, formal intervention, and more complete notices. However, it does not change the answer to the most important question at all, since public hearings in a Site Consultation would remain discretionary.
Doubts also remain about how much participation will be allowed in environmental processes, since neither the categorical exclusion nor the EA admits third parties, and a DIA would have a public hearing only “when applicable.” There are also doubts about the priority track, which displaces the Environmental Public Policy Act.
Finally, the Code is completely silent on data centers and other similar new-technology projects. It does not require a company to disclose the location before filing a project, nor to submit reports on water and energy use, as some states and the European Union already require, as we noted in our previous post.
And what if the data center were to be built on dry land? The process could be different. The Code starts from a scale of land-use intensities: if the proposed use does not exceed the maximum intensity for the cadastral parcel, the process is ministerial, with no Site Consultation or public hearing (Arts. 12.03 to 12.05). The Senate describes that anyone who is going to operate a permitted use could file a use declaration in the Unified Information System, pay the fee, and open the same day, with no prior inspection or discretionary approval. The Code says nothing about where on the scale a data center would fall.
In addition, as we read it, a construction project under the Consolidated Construction Permit automatically qualifies as a categorical exclusion and is supported by a sworn self-certification, unless the property is in certain areas, such as flood zones, wetlands, protected areas, or the maritime-terrestrial zone (Art. 12.16). The list does not include the project’s size or its water or energy consumption.
What Can You Do?
For now, this bill is not law, so keep following it in the news, the media, and on social media. However, if it is approved, you will have the opportunity to speak formally when the comment period for the Unified Regulation opens. If that happens, regarding AI data center projects or other similar projects, these are questions that should be asked:
- Who is an “adjoining property owner” when a project is in the waters of the sea?
- Will public hearings be required for marine infrastructure projects or projects with high energy or water consumption?
- What thresholds trigger a DIA instead of an EA?
- Will companies be required to disclose water and energy consumption, as in the EU?